On this page3
The GDPR is one of the most comprehensive yet challenging regulatory frameworks that organizations will need to address in 2026.
The General Data Protection Regulation (GDPR) is a worldwide privacy regulation established by the European Union to regulate how organizations collect, manage, and secure personal information.
Under this law, which took effect on May 25, 2018, data subjects have the right to choose how their Personally Identifiable Information (PII) is collected, used, and shared.
In this detailed article, we will examine the essential components of GDPR and how small businesses can ensure compliance to thrive in the digital world.
GDPR For Small Businesses
There are no exceptions to the EU GDPR, regardless of a company’s size. Businesses that handle Personally Identifiable Information (PII) must comply with the General Data Protection Regulation (GDPR).
Under the GDPR, small business owners cannot collect an individual’s contact information via an effective business card, LinkedIn page, or general conversation without obtaining their explicit consent.
Even if the details come from networking materials created with a business card maker, businesses must still ensure they have permission before storing or using that contact information.
Therefore, small enterprises must be GDPR compliant and appoint a Data Protection Officer (DPO) to handle any personal data they may collect.
However, most US-based small firms may be exempt from specific GDPR requirements. Some small enterprises may be exempt from additional record-keeping requirements if they only occasionally handle the personal data of EU citizens.
Read more on: How to Know if Your Lawyer is Selling You Out.
Moreover, small businesses that provide products or services infrequently to EU customers can qualify for exemptions.
GDPR Compliance Requirements for Small Businesses
Companies must comply with the GDPR as required by law. The most crucial prerequisites for small firms are as follows:
a. Collection and Processing
Under the GDPR, personal information must be collected truthfully, legally, and securely. Article 6 mandates that data controllers and enterprises establish a legal basis for processing personal data, whether they are large corporations or small firms employing fewer than 250 people.
A contract must be in place; the data subject must provide informed consent, or an organization’s legitimate interest that poses the least risk to data subjects' rights must exist.
b. Consent
According to Article 7, before processing, obtaining, storing, or using any data, organizations must obtain the informed, voluntary permission of each data subject.
c. Security
Articles 23, 30, and 32 require companies to use appropriate data protection measures to protect consumer privacy and prevent data loss or disclosure.
d. Data Breach Alert
Controllers are required by Articles 33–34 to notify Supervisory Authorities of any data breaches within 72 hours. The specifics of the breach, including its nature and the approximate number of affected data subjects, must be included in this notification.
e. Data Protection Impact Assessments (DPIAs)
GDPR-compliant businesses must conduct DPIAs under Article 35 to identify and mitigate threats to consumer data. To ensure ongoing GDPR compliance, Article 37 requires small firms to designate one or more Data Protection Officers.
6 Steps To Implement GDPR Compliance for Small Businesses
With a clear understanding of the GDPR requirements, it is imperative to implement them in real-world business environments. The implementation process involves a series of steps that make it easier to comply with GDPR. Here are six steps you can take to comply with GDPR:
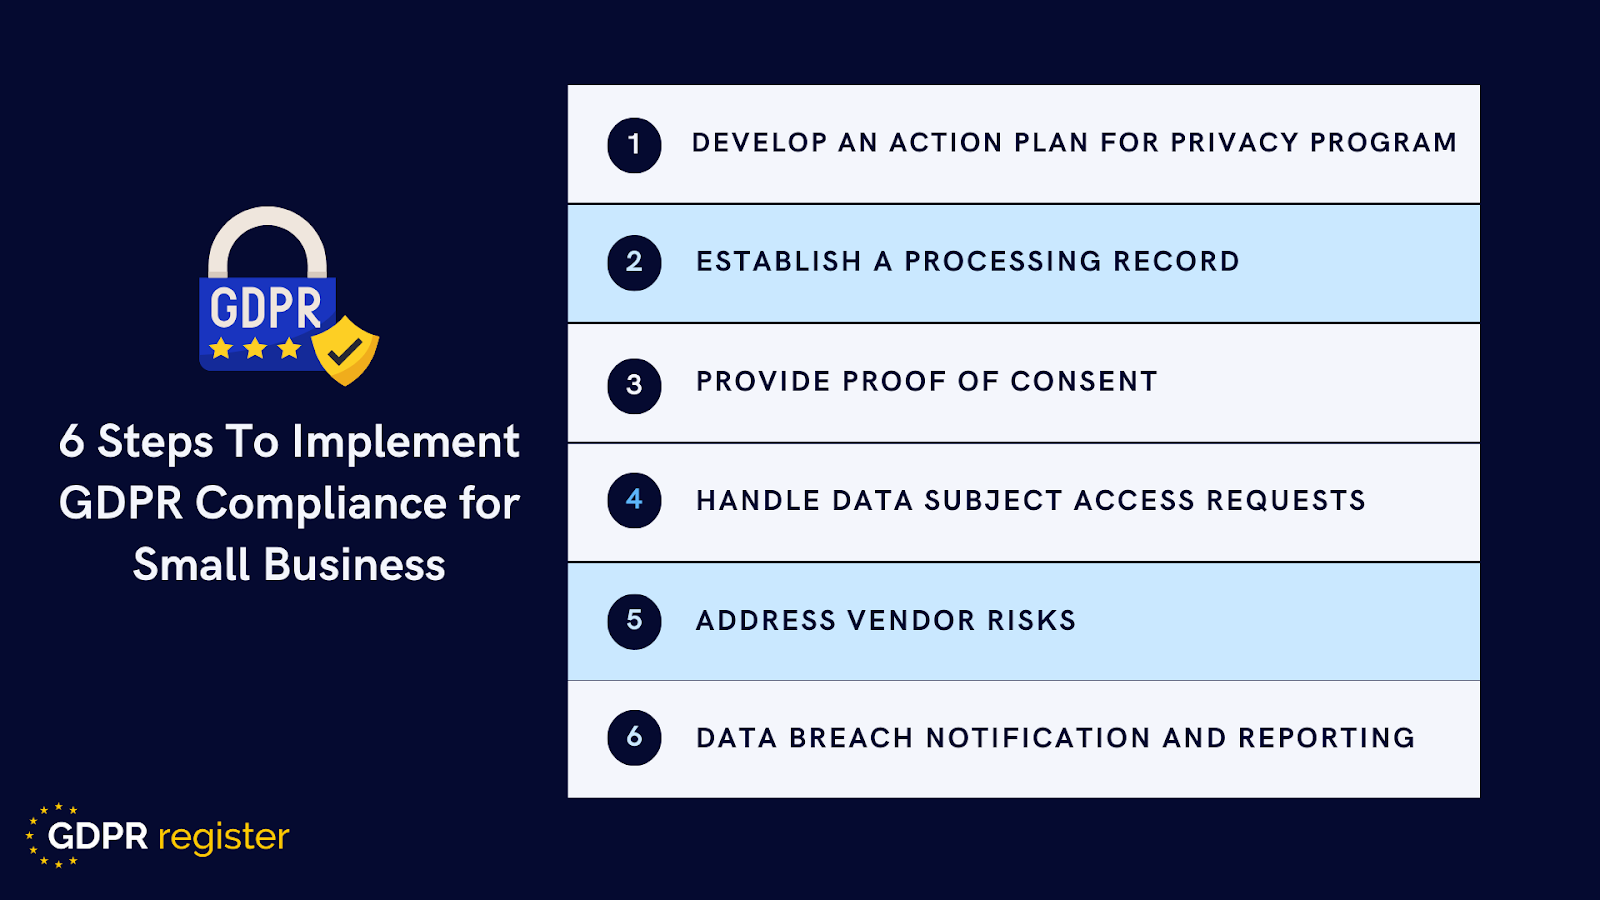
Image Source: GDPR Register
1: Develop an Action Plan to Implement a Privacy Program
For small businesses, the first step in complying with GDPR is to evaluate their present privacy program.
Determine whether the organization has previously complied with GDPR by conducting a readiness assessment.
Then, evaluate risk and data privacy issues by conducting a risk assessment, such as a Data Protection Impact Assessment.
These assessments lead to the development of a compliance action plan to protect high-risk activities in the future.
2: Establish Processing Record
Identify and map the consumer data gathered to determine what was collected and why.
Under Article 30 of the GDPR, controllers and their representatives must maintain records of processing activities.
Additionally, companies need to audit their data and service providers to determine what data is collected, how it is processed and transmitted, and which suppliers use it.
This action will help small businesses stay up to date.
A unified single source of truth for all personal data processing the company stores.
3: Provide Proof of Consent
Regarding consent, small businesses are concerned about demonstrating to authorities that they have requested and received proper permission.
As previously stated, enterprises must demonstrate that they obtained free and informed consent from data subjects through a clear, explicit request.
When creating permission request forms, ensure they are readily accessible and easy to understand. Permission requests should not be hidden in lengthy contracts or terms of service; they should be presented through a simple opt-in method that clearly identifies the request for consent. Furthermore, data subjects have the right to withdraw their permission at any time. Therefore, a consent request form should explain how they can withdraw consent in the same way they provided it.
So, while creating a consent request form, consider:
Review the procedure for obtaining permission and ensure it is compliant with the GDPR.
Provide clear descriptions of permission requests in privacy rules and notifications.
Provide customers with specific consent options, such as communication frequency or medium.
4: Handle Data Subject Access Requests
Data Subject Access Requests (DSARs) are expected to increase for small businesses as they receive more customer authorization.
According to the GDPR, consumers have several fundamental rights.
They can exercise these rights at their discretion, including the right to access, correct, delete, and export data.
Any small business that collects consumers’ personal information must be prepared to handle these requests, whether they are submitted manually or automatically.
When submitting a data subject request, you must complete three stages.
Making a request: A data subject must be able to submit a request manually or electronically in a standard manner. Prepare a request form that collects the information needed to process the request so they don’t have to provide excessive details.
Validation: One of the most challenging aspects of accepting data subject requests is determining who made the request. To ensure personal data is released to the correct individuals, take time to verify that the person making the request is the intended recipient.
Fulfillment: Once a request has been received and confirmed, provide the desired information within one month. However, if small enterprises receive an excessive and complicated number of requests, the GDPR allows them to extend the completion time to three months.
5: Address Vendor Risks
It is common for a small firm to have multiple suppliers involved in its operations and procedures. However, they may not be GDPR compliant. Article 28 of the GDPR requires organizations to enter into data processing agreements between data controllers and processors to ensure compliance with GDPR obligations.
As the marketing, product development, and IT teams continue to review and collaborate with third-party vendors, ensure they all satisfy the same GDPR compliance standards. Take the time to compile a list of suppliers that receive data and determine if they are controllers or processors.
As the supplier list outgrows what a small team can monitor by hand, supplier risk management software standardizes how risk scores, audit evidence, and renewal cadences are tracked across the portfolio.
Once completed, small companies can create a strategy to ensure that both parties are prepared for the GDPR. Businesses seeking to enhance their online presence while ensuring GDPR compliance should explore affordable web hosting options that provide the necessary security, reliability, and compliance features.
6: Data Breach Notification and Reporting
Lastly, the GDPR specifies how a breach of personal data should be reported and defines it in Article 4 as “loss, alteration, unauthorized disclosure, or access to personal data resulting from a breach of security.”
When this type of breach occurs, it must be reported to regulatory authorities within 72 hours, and the affected data subject must be informed. At a minimum, small firms that suffer a data breach must include the following in their notification:
Describe the nature of the personal data breach.
Provide the name and contact information of the DPO or other points of contact to acquire further details on the breach.
Describe the potential repercussions of the personal data leak.
A description of the steps taken or intended to resolve the personal data breach, including efforts to minimize any negative consequences.
Final Words
Due to the urgency and importance of compliance, navigating GDPR is critical for small businesses. This guide emphasizes the importance of compliance regardless of business size, outlines essential GDPR requirements, and provides a six-step process for successful implementation.
These steps help determine privacy programs, maintain processing records, and ensure consent is collected correctly. Based on these steps, GDPR is more than a legal obligation; it is a way to safeguard trust and personal information. By adopting GDPR practices, small companies can avoid penalties, enhance their credibility, and ensure a lasting presence in the digital market.
Compliance is an ongoing process that requires constant vigilance regarding regulatory changes and emerging privacy issues.